
Prompts are not permissions.
Your support agent can be talked into a $900 refund. Warden checks every action an agent proposes against rules you write, holds the risky ones for a person, and records each decision in an audit log you can verify.
Made for n8n builders and agencies automating for small businesses, and for small teams whose agents touch money, email or production data.

Works with
n8n MCP LangChain CrewAI Python JavaScript any HTTP client
It already happens.
Three public cases where an agent did real damage. In each one, the agent had access it should not have used without asking.
- July 2025. Replit's coding agent deleted SaaStr's production database during a code freeze, wiping records on 1,206 executives. The data was later restored from a rollback. The Register
- April 2026. A coding agent at PocketOS found a broad Railway API token and deleted the production volume and its backups in about nine seconds. Railway recovered the data afterwards. The Guardian
- February 2024. Air Canada's support chatbot made up a refund policy. A tribunal ordered the airline to honour it and pay C$650.88 plus interest and fees. The Guardian
How it works
Your agent asks before it acts. Warden answers from your policy file, so the model can't argue with the decision.
The agent proposes the action.
POST /v1/actions
{ "agent_id": "refund-bot", "tool": "refund.create",
"params": { "order_id": "ORD-1051", "amount": 900 } }A person approves in the web queue. Slack can notify them through a webhook.
The agent executes with the frozen payload. A changed amount or a second attempt is refused and logged.
POST /v1/actions/{id}/execute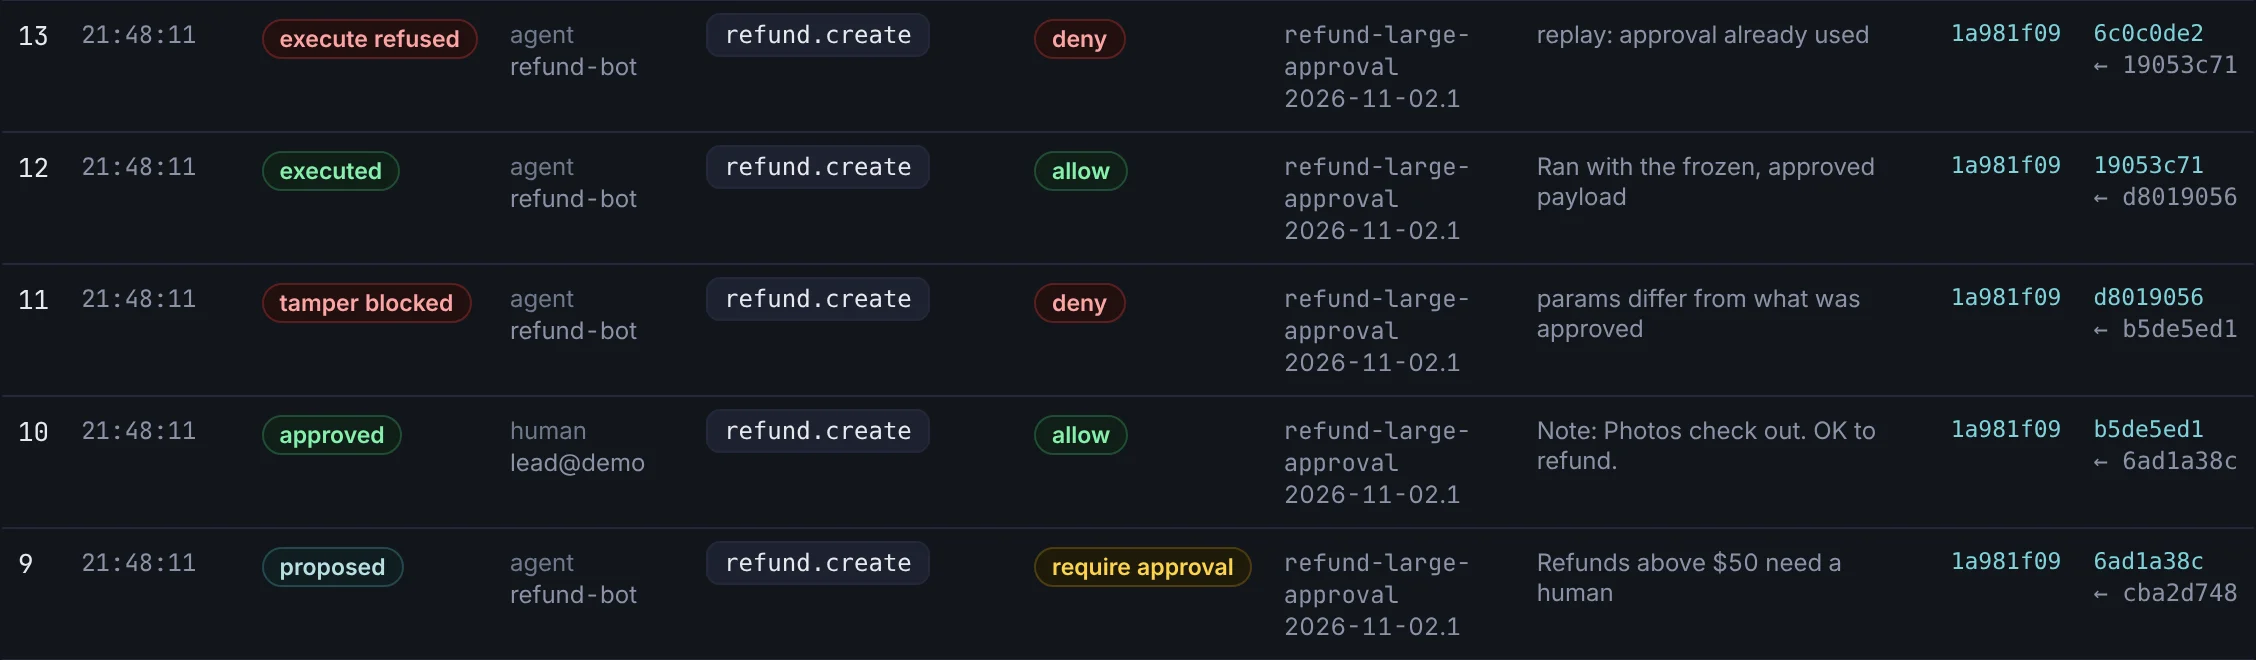
What works today
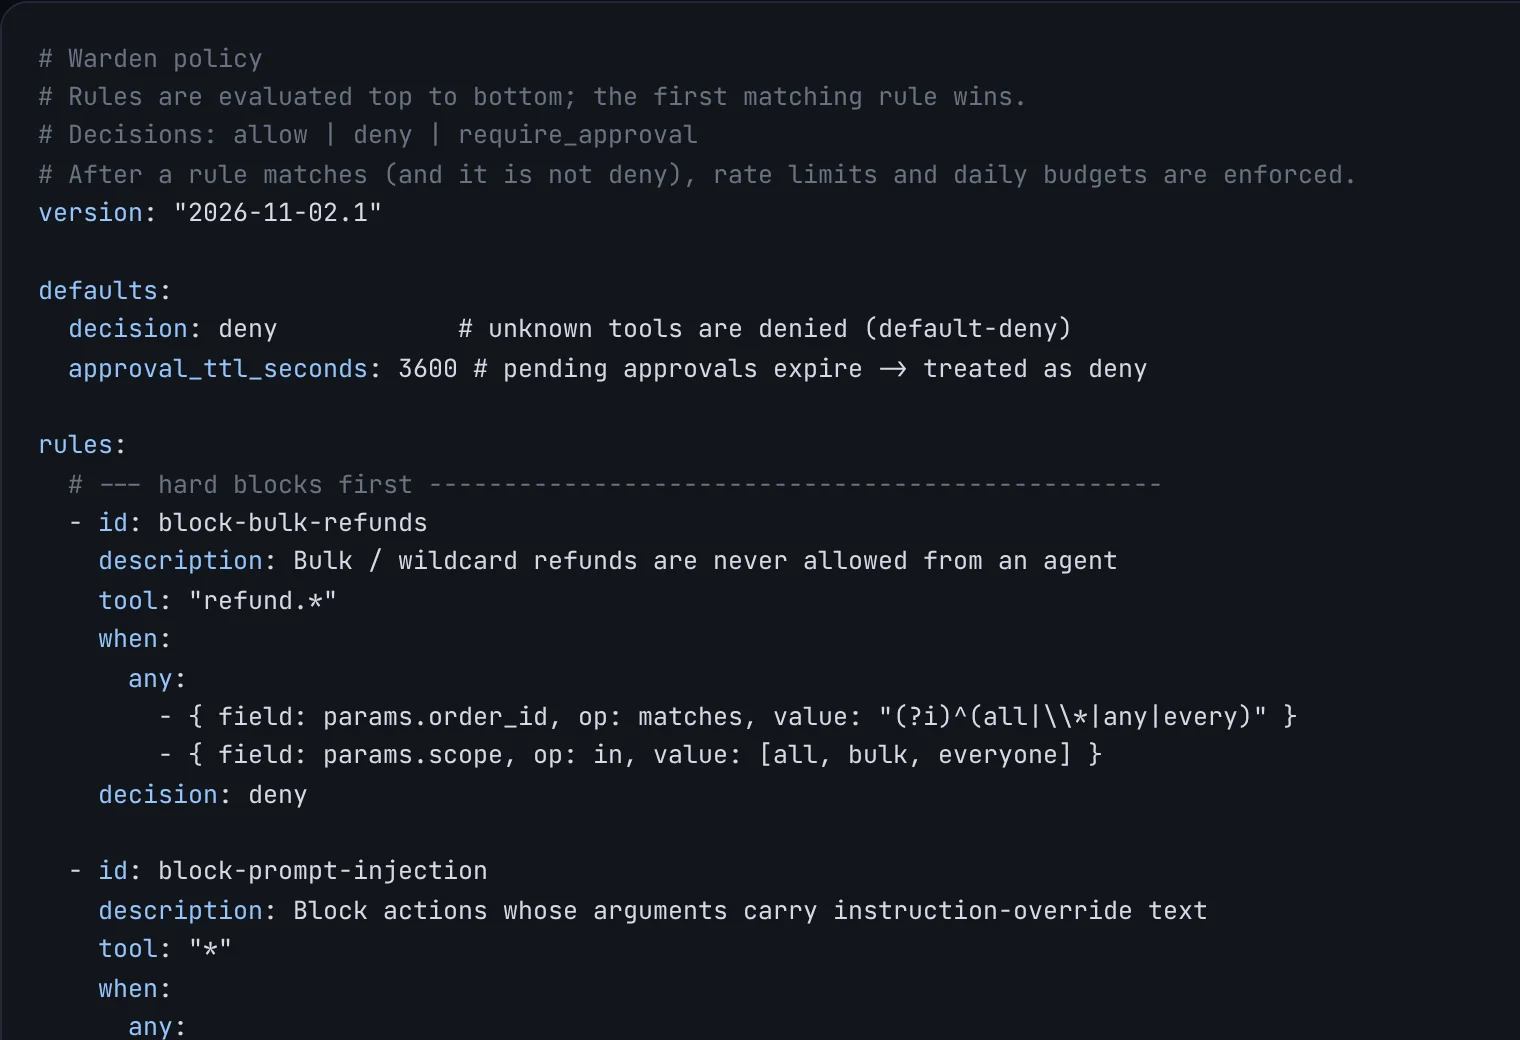
- One YAML policy: allow, deny or require approval. The first matching rule wins and unknown tools are denied.
- Daily budgets and rate limits per agent and tool.
- Approvals frozen to the exact payload by hash. Each one works once.
- Approvals expire after a window you set, and an expired request counts as a denial.
- A rule that blocks arguments carrying "ignore previous instructions" style text.
- A hash-chained audit log you can re-verify and export as CSV or JSON.
- A web approval queue, plus Slack notifications through a webhook.
- Python and JavaScript SDKs, an MCP gateway and a step-by-step n8n guide.
Self-host
Warden runs on your own machine with Python 3. Early-access members get the repository first. From the project folder, one command starts the dashboard and a demo refund bot that fills the queue:
./run.sh
# dashboard  http://localhost:8080
# API docs http://localhost:8080/docsEdit policy.yaml to write your rules, and point your agent at POST /v1/actions. Set SLACK_WEBHOOK_URL to get a Slack message when something waits for approval. The repository ships with 8 automated tests for policy, budgets, prompt injection, tamper, replay and the audit chain. All 8 pass on this build:
.venv/bin/python -m pytest -q testsPricing
Hosted prices are placeholders until those plans launch. Design partners get free setup, and we write your first policy with you.
Join early access
Tell us what your agent touches and we'll help you fence it.
Questions
Isn't a good system prompt enough? No. A prompt is a suggestion to a model, and text injected into a ticket or an email can override it. Warden decides outside the model with rules that don't change when the conversation does.
How is this different from n8n's Send and Wait? Send and Wait pauses one workflow. Warden keeps one policy across every agent and workflow, with amount thresholds, budgets, rate limits, approvals tied to the exact payload, and a history you can verify.
What stops the agent from changing the amount after I approve? The approved parameters are hashed and frozen. At execute time they must match the hash, or Warden refuses and logs a tamper event. Each approval works once.
Does it slow my agent down? Policy checks run locally and take milliseconds. Only actions your rules send to a person wait for one.
What happens if nobody approves? The request expires after the window you set and counts as a denial. The agent is told it wasn't approved.
Where does my data live? When you self-host, in a SQLite file on your own server. Hosted plans aren't live yet.
Is the audit log tamper-proof? It's tamper-evident. Each entry includes the hash of the one before, the database refuses edits and deletes, and anyone can re-verify the chain. Signing is on the roadmap.
Is it open source? Not yet. Self-hosting is free for early-access members, and the license will be settled before a public release.